Phala Network is moving past Web3 privacy to build Confidential AI tools using hardware-based Trusted Execution Environments and GPU TEE. The project wants to protect AI models and user data while making off-chain computation verifiable.
Phala Network is betting that the next phase of AI and blockchain will need privacy at the hardware level, not just through cryptography or smart contracts. The team is now focused on Confidential AI. They use Trusted Execution Environments (TEE) and GPU TEE to keep sensitive models, data, and agent runtimes hidden from cloud providers and admins. At the same time, they offer cryptographic proof that workloads ran as claimed.
This is a big change from Phala's early days as a Web3 Confidential Computing network on Polkadot. The project has dropped its parachain model, moved to Ethereum Layer 2, and is now building products like Phala Cloud, dstack, and GPU TEE support. These tools target AI developers and businesses that need verifiable privacy for large-scale inference and agent operations.
In September 2026, Phala reported a record 112.21 billion tokens processed in 24 hours, highlighting real-world demand for Confidential AI workloads on its TEE infrastructure.
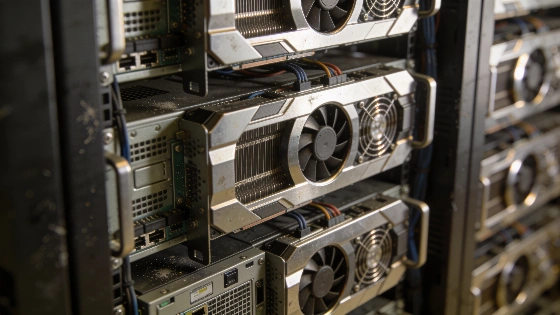
Hardware-protected AI is now at the heart of Phala's strategy. Most cloud AI services ask users to trust that their models, prompts, and data stay private after upload. Even if data is encrypted in transit, it is exposed during use to anyone with high-level access to the server. Phala's answer is to run AI workloads inside hardware-isolated environments. They use Intel TDX, AMD SEV-SNP, and NVIDIA GPU Confidential Computing. This setup blocks even infrastructure operators from seeing code or data while it runs.
Phala Cloud, the project's Confidential Computing platform, lets developers deploy AI models and agents in Confidential VMs that combine CPU and GPU isolation. The platform supports Docker-based workloads. It ties hardware, VM images, and app settings to attestation evidence, so users can check the environment before releasing sensitive keys or data. When GPU TEE support arrived, Phala targeted NVIDIA H100 and H200 hardware. The goal was to bring confidential AI inference closer to native speed. This focus on GPU-based confidential computing sets Phala apart, as shown in its official infrastructure documentation.
Phala's SayGM product, launched in 2026, takes confidential workloads further. It routes all supply-side operations-including routing operators and the attestation layer-into Phala Cloud. Requests go through hardware-attested confidential VMs, with images locked by digest. This ensures only verified environments handle sensitive AI tasks. The dstack framework, open-sourced under Apache 2.0 and hosted by the Linux Foundation, forms the backbone of this setup. Phala Cloud acts as a managed layer for provisioning, scaling, monitoring, and billing, but never gets access to workload memory or storage keys.
Phala began as a Polkadot parachain and has since expanded across chains, now serving significant token volumes for AI tasks. The network's evolution reflects a broader industry shift toward privacy-preserving AI inference and verifiable compute.
Running code in a TEE is not enough. Users need proof that the right code is running on the right hardware. Phala's open-source dstack runtime handles deployment, authentication, key management, and attestation. It binds application identity to hardware and software state. This lets outside parties check that an AI agent or model is running in a trusted environment before giving it access to private data or permissions.
dstack supports several attestation paths, including Intel TDX, AMD SEV-SNP, TPM, AWS Nitro NSM, and NVIDIA Confidential Computing. In 2026, Phala and OPPO extended this to Kubernetes Pods, so remote attestation can happen at the container level for AI workloads. This creates a chain of trust from hardware to application, cutting down the need to trust cloud providers or server admins.
Token mechanics and ecosystem shift
Phala's native token, PHA, was first used to reward TEE resource providers, support staking, and help with governance. After moving to Ethereum L2 and shifting to Confidential AI, PHA's technical setup and value-capture methods are changing. The 2025 plan brought staking, governance, computing rewards, and asset transfers into the new system. Still, the token's use is tied to network participation and resource incentives, not direct price guarantees.
Phala's pivot matches a wider trend in privacy infrastructure. Projects like Zama are also working on encrypted computation and confidential DeFi. As reported earlier, demand for privacy-preserving computation is rising in DeFi, AI, and business, but technical and economic hurdles are still high.
Phala's Confidential AI model aims to protect not just user inputs, but also model weights, prompts, intermediate states, and agent permissions. For example, a business AI assistant running on Phala Cloud can process internal financial data and private models without exposing them to the cloud provider. The same setup lets AI agents manage wallets, code repositories, or on-chain accounts in a hardware-protected environment. Attestation gives verifiable proof of runtime integrity.
Even with these advances, Phala faces real hurdles. High-end GPUs like H100 and H200 are expensive, and Confidential Computing adds performance overhead. TEE trust boundaries are not perfect-hardware bugs, software flaws, and key management issues can still break security. Market demand for Confidential AI is growing, but the number of users willing to pay for privacy and verifiability is still small, especially in regulated fields like finance and healthcare.
Phala's technical roadmap now focuses on building verifiable private computing environments for AI and Web3, not just extending blockchain privacy. The project's future depends on delivering practical, scalable Confidential AI infrastructure that developers and businesses can trust and afford. In September 2026, SOON made a strategic investment in Phala's TEE GPU cluster. This move showed ongoing ecosystem growth around private AI agents and verifiable compute, and reinforced the network's push for infrastructure expansion.
Phala Network's evolution shows how privacy and trust in AI and blockchain are getting more complex. By moving sensitive computation off-chain but anchoring trust in hardware and cryptographic attestation, Phala is betting that the future of confidential computing will rely on verifiable execution, not just code audits or network consensus. The project's choice to leave its old architecture and adopt new hardware standards is a practical response to real-world AI privacy needs. The real test will be whether its infrastructure can deliver both security and usability as the market grows.
Trusted Execution Environments (TEE) are a type of hardware-based security that isolates code and data from the rest of the system. This lowers the risk of exposure to privileged users or attackers. TEE can give strong guarantees for runtime confidentiality and integrity, but its strength depends on the hardware, software stack, and how it is run. Remote attestation is key. It lets outside parties check that a workload is running in a real TEE with the right setup. Still, TEE does not remove all risks-side-channel attacks, hardware bugs, and supply chain problems can still break security. For users and developers, knowing the limits and dependencies of TEE-based privacy is crucial when looking at Confidential AI and blockchain infrastructure.